CISA Warns of Seven Actively Exploited Security Flaws as Hackers Target AI Infrastructure
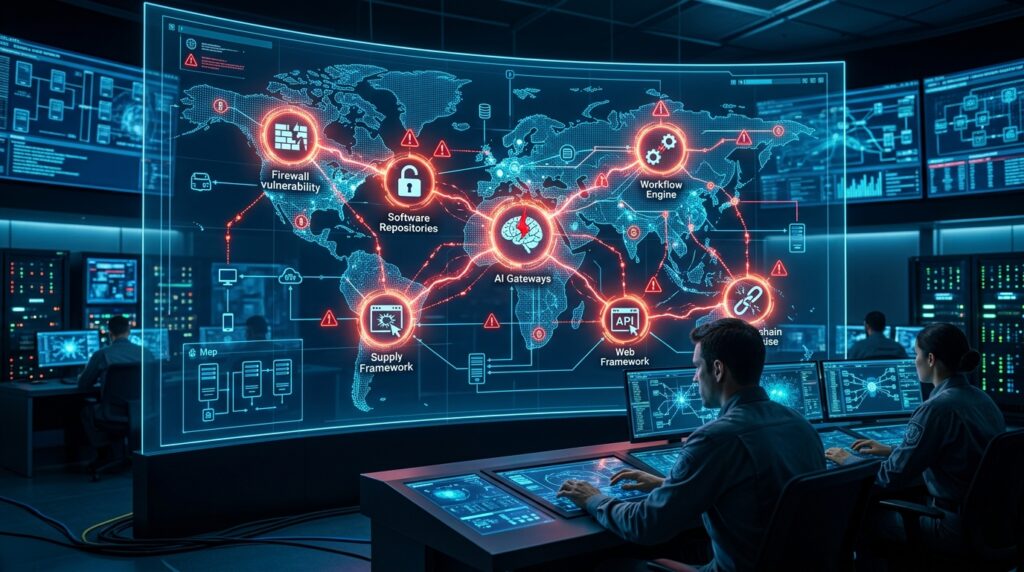
Cybercriminals are actively exploiting a new group of serious software vulnerabilities, and some of the attacks are being used to install cryptocurrency miners, create hidden access points, steal credentials, and take control of AI infrastructure.
The U.S. Cybersecurity and Infrastructure Security Agency, better known as CISA, has added seven vulnerabilities to its Known Exploited Vulnerabilities, or KEV, catalog after evidence showed that attackers are already using them in real-world attacks.
The affected technologies include products from SonicWall, Sangoma, JFrog, Starlette, Kestra, and LiteLLM.
For businesses running any of these systems, this is not just a theoretical security warning. Some of the vulnerabilities are already being weaponized.
The Seven Vulnerabilities Added by CISA
1. SonicWall SMA 1000 — CVE-2026-83548
Severity: Critical — CVSS 10.0
This flaw affects SonicWall SMA 1000 appliances.
An attacker may be able to exploit the vulnerability remotely without logging in and gain access to sensitive functions inside the system.
Because SonicWall appliances are commonly used for secure remote access, a compromise could potentially give attackers an important entry point into a company’s network.
2. SonicWall SMA 1000 — CVE-2026-83549
Severity: High — CVSS 7.8
This second SonicWall vulnerability can allow an authenticated administrator account to execute operating system commands.
If attackers first gain administrative access, they could potentially use the vulnerability to take deeper control of the affected system.
SonicWall has already confirmed that it investigated activity indicating exploitation of both vulnerabilities.
3. Sangoma Switchvox — CVE-2026-9586
Severity: Critical — CVSS 9.3
This vulnerability affects Sangoma Switchvox systems.
It is an SQL injection flaw that could allow an attacker to send a specially crafted request to the system’s PostgreSQL database.
The attacker may be able to manipulate the database and, in some cases, move further toward remote code execution.
Researchers have observed attackers exploiting the vulnerability to deploy reverse shells.
A reverse shell effectively gives the attacker remote command-line access to the compromised server.
4. JFrog Artifactory — CVE-2026-82329
Severity: Critical — CVSS 9.8
This flaw affects JFrog Artifactory.
Under certain default configurations, an attacker with network access may be able to bypass authentication and obtain administrator-level privileges.
That is particularly dangerous because Artifactory is often used by software development teams to manage packages, applications, and development artifacts.
Attackers exploiting this vulnerability have reportedly created administrator tokens and used them to investigate users, credentials, groups, and federated access environments.
5. Starlette — CVE-2026-48710
Severity: Medium/High — CVSS 6.5
Starlette is a Python framework frequently used in modern web applications and APIs.
The vulnerability involves HTTP request and response smuggling.
In certain configurations, an attacker could manipulate how a URL is reconstructed and potentially bypass authentication protections that rely on URL paths.
The vulnerability becomes even more dangerous when combined with other security flaws.
Researchers previously found that it could be chained with a LiteLLM vulnerability to bypass authentication and potentially achieve remote code execution.
6. Kestra OSS — CVE-2026-49869
Severity: Critical — CVSS 10.0
This is one of the most serious vulnerabilities on CISA’s latest list.
Kestra is an open-source orchestration platform used to automate workflows.
The vulnerability could allow an unauthenticated attacker to create and execute malicious workflows remotely.
Microsoft reported that attackers likely exploited this vulnerability during an incident in June 2026.
Once inside, the attackers reportedly:
- Established a reverse shell
- Investigated the Docker container environment
- Attempted to evade security defenses
- Installed a cryptocurrency miner
- Collected data from the compromised system
The attackers were effectively able to use the victim’s infrastructure for their own operations.
7. LiteLLM — CVE-2026-59822
Severity: High — CVSS 8.8
LiteLLM is becoming increasingly popular as a gateway for connecting applications to different large language models and AI providers.
This vulnerability affects LiteLLM’s Model Context Protocol, or MCP, Streamable HTTP endpoint.
An attacker may be able to use an arbitrary Bearer token to create what appears to be an authenticated MCP session.
Security researchers have already observed attempts to exploit the vulnerability against exposed systems.
AI Infrastructure Is Becoming a Major Cybercrime Target
One of the biggest lessons from these attacks is that AI infrastructure is quickly becoming a valuable target for hackers.
Attackers are no longer focused only on traditional servers, databases, and employee computers.
Platforms supporting artificial intelligence applications can contain extremely valuable information, including:
- AI API keys
- Cloud credentials
- Model configurations
- Provider access tokens
- Backend database credentials
- Internal application data
- LLM provider endpoints
- Authentication tokens
Once attackers gain access, these credentials can potentially provide access to expensive AI services or additional parts of the company’s infrastructure.
Hackers Are Installing Cryptocurrency Miners
Some of the attacks uncovered by Microsoft involve the installation of XMRig, a popular cryptocurrency mining application frequently abused by cybercriminals.
Instead of purchasing expensive computing resources themselves, attackers compromise servers and use the victim’s CPU or GPU resources to mine cryptocurrency.
This can result in unusually high cloud bills, slower system performance, higher electricity usage, and increased hardware workload.
Attackers have even been observed searching compromised systems for competing cryptocurrency miners and shutting them down so they can use the computing resources themselves.
Hackers Are Also Stealing AI Credentials
The attacks against LiteLLM environments show another important threat.
Attackers reportedly accessed PostgreSQL databases supporting LiteLLM and searched tables containing information about:
- AI models
- Provider API keys
- Proxy-issued virtual keys
- AI provider endpoints
- Authentication information
These credentials can potentially allow attackers to abuse commercial AI services, impersonate applications, or move deeper inside a company’s infrastructure.
Attackers Are Creating Persistent Access
Getting inside a system is only the first step.
Cybercriminals also want to make sure they can return later.
Researchers observed attackers modifying files such as:
~/.ssh/authorized_keys
This allows attackers to install their own SSH keys and potentially regain access even after some passwords are changed.
Attackers were also observed using command-and-control infrastructure and techniques designed to avoid detection.
Other AI Platforms Could Face Similar Risks
Security researchers are warning that this trend goes beyond LiteLLM and Kestra.
Other AI-related technologies that could attract attackers include platforms such as:
- Flowise
- LangChain
- Langflow
- ChromaDB
- Ollama
- Marimo
- MCP servers
- RAGFlow
These platforms frequently connect directly to databases, cloud infrastructure, AI providers, internal company data, and authentication systems.
That makes them valuable targets.
RAGFlow Systems Are Also Being Targeted
Microsoft has also investigated attacks involving exposed RAGFlow environments.
Attackers are suspected of exploiting several vulnerabilities to gain persistent access and steal large language model provider keys and related configuration information.
The goal appears similar across many of these campaigns:
Steal credentials, maintain access, and make money from compromised infrastructure.
What Businesses Should Do Now
Organizations using any of the affected technologies should treat these vulnerabilities as urgent.
1. Patch affected systems immediately
Check whether your environment uses:
- SonicWall SMA 1000
- Sangoma Switchvox
- JFrog Artifactory
- Starlette
- Kestra
- LiteLLM
Install available security updates as quickly as possible.
2. Do not expose management systems directly to the internet
Administrative dashboards, AI gateways, databases, orchestration systems, and developer platforms should not be publicly accessible unless absolutely necessary.
Use VPNs, firewalls, private networks, and access-control policies.
3. Rotate credentials after a suspected compromise
If an affected system was publicly exposed, consider rotating:
- API keys
- Administrator credentials
- SSH keys
- Database passwords
- Cloud access tokens
- AI provider credentials
Patching alone may not remove access already established by an attacker.
4. Look for unusual cryptocurrency mining activity
Watch for unexpected spikes in:
- CPU usage
- GPU usage
- Cloud bills
- Server load
- Network traffic
These can sometimes indicate unauthorized mining.
5. Monitor AI infrastructure like critical infrastructure
Businesses should no longer treat AI applications as simple experimental tools.
If an AI platform has access to internal databases, APIs, cloud systems, customer information, or company credentials, it should receive the same security protections as other critical infrastructure.
6. Review SSH access
Administrators should inspect SSH authorized-key files for unknown entries and monitor for suspicious login activity.
7. Review logs for unusual administrative activity
Look for unexpected administrator accounts, newly created tokens, unusual workflows, unauthorized database queries, or unexplained configuration changes.
CISA Patch Deadlines
Federal Civilian Executive Branch agencies have been directed to prioritize remediation of the vulnerabilities.
Most of the flaws are expected to be addressed by September 5, 2026.
The Starlette and LiteLLM vulnerabilities have a later remediation deadline of September 16, 2026.
Private companies are not necessarily bound by the same federal deadlines, but CISA’s decision to place a vulnerability in the KEV catalog should be treated as a strong warning.
These are vulnerabilities attackers are known to be exploiting.
What This Means for Businesses
The cybersecurity landscape is changing as companies rapidly adopt AI.
AI platforms are increasingly connected to some of the most valuable parts of a company’s technology environment: databases, cloud accounts, APIs, internal documents, automation systems, and AI provider credentials.
That means attackers now have another attractive entry point.
A vulnerable AI gateway could eventually become a pathway into much more than an AI application.
Organizations should therefore start treating AI infrastructure as part of their main cybersecurity perimeter.
Aqyreon’s Take
The biggest takeaway from CISA’s latest warning is simple:
Installing AI tools is easy. Securing the infrastructure behind them is becoming much harder.
Hackers are actively searching for exposed AI systems, vulnerable gateways, orchestration platforms, and poorly protected APIs.
And their goals are practical: steal credentials, gain persistent access, compromise backend systems, or turn someone else’s servers into cryptocurrency mining machines.
Businesses adopting AI should therefore ask more than:
“What can this AI tool do for us?”
They should also ask:
“What systems and credentials can this AI tool access if someone compromises it?”
That question could become one of the most important cybersecurity questions businesses ask as AI adoption continues to grow.